Cyber Brief · Article
Patch, protect, prevent: what the ACSC's critical alert means for you
efex
Published · Last updated
On 17 November, Australia's cyber agency published a critical alert: Act Now. More security flaws are being found, and attackers have exploited some of them within 48 hours of a fix being released. A monthly patching cycle can't keep up. The ACSC's advice comes down to three words: patch, protect, prevent. Here's what each one means for you, and what to ask your IT team or provider this week.[1]
Why has the ACSC issued this alert?
The Australian Cyber Security Centre (ACSC), part of the Australian Signals Directorate (ASD), warned that significant flaws are being found across many technologies. It continues to respond to incidents where attackers gained access through systems that hadn't been updated.[1]
In those incidents, the ACSC said, attackers "exploited individual vulnerabilities or combined several weaknesses to gain broader access, steal data or take control of systems". Automated and AI-enabled tools are helping attackers find and exploit flaws faster, across more systems. Organisations have less time to respond. The ACSC's message was clear: "Organisations should prepare for more frequent security updates and shorter timeframes for action."[1]
Why is the time to act getting shorter?
Two things are shrinking the time available to respond: more flaws are being found, and automated tools and AI are helping attackers move faster.
The number of publicly reported security flaws rose 30% in 2025-26, according to ASD's latest Annual Cyber Threat Report. ASD has seen most flaws exploited within two weeks, and some within 48 hours of a fix being released. It expects AI tools to shorten that window again over the next year.[3]
30%
Source: ASD Annual Cyber Threat Report 2025-26
48 hours
Source: ASD Annual Cyber Threat Report 2025-26
ASD puts it this way: "In the past, defenders had months to patch, now they have days, sometimes only hours."[3]
You can't rely on a monthly patching cycle for internet-facing systems any more. It can leave a known weakness open for weeks after a fix is available, while attackers need only days.
Put the questions below to your IT team or provider this week. If they can't give you a clear answer, talk to our cyber security team. We're offering a free cyber audit until 30 November.
1. Patch: how quickly are urgent fixes applied to your systems?
The ACSC asks organisations to speed up patching, turn on automatic updates where appropriate, and "confirm suppliers can promptly patch systems they manage on your behalf".[1]
Start with anything that can be reached from the internet, such as firewalls, VPN and remote access, email and websites. These systems need the fastest response because they're directly exposed. We recommend applying urgent fixes to them within 48 hours of release.
Suppliers matter here too. If an IT provider, software vendor or equipment supplier manages systems for you, their patching speed is your patching speed. That includes the tools your IT provider uses to manage your systems remotely. They have wide access, so they need the same attention. Charles Mann covers what to ask critical suppliers in his piece on supply chain cyber security.
If a fix can't be applied straight away because it needs a restart during business hours, needs testing first or hasn't been released yet, don't just wait. The ACSC's advice is to "assess the risk, restrict exposure and implement temporary security controls until remediation is complete."[1] In practice, that could mean limiting access to the system until the fix is in place.
Ask your IT team or provider: How long did it take to apply last month's urgent fixes to our internet-facing systems? Which suppliers manage systems for us, and how quickly do they apply fixes, including to the tools they use to manage ours?
A good answer sounds like: "Last month, every urgent fix on our internet-facing systems was applied within 48 hours, and we can show you the report. Our suppliers have agreed to the same timeframe in writing, including for the tools they use to manage our systems. Where a fix couldn't be applied straight away, we restricted access until it was."
2. Protect: how much of your organisation can attackers see?
The ACSC asks organisations to find and reduce unnecessary exposure of systems and services on the internet, and to review and strengthen sign-in and access controls, including multifactor authentication. It also asks them to address old systems, because "unsupported systems are easy targets".[1] That means replacing technology that no longer gets security fixes, or keeping it off the internet and away from other systems until you can.[3]
The less you expose to the internet, the less there is for attackers to find and test. Multifactor sign-in adds protection when a password is stolen. Older technology creates a different problem: once security updates stop, newly found flaws stay unfixed.
Windows Server 2016, for example, gets its last regular security fix on 12 January 2027. If you're still running it, now is the time to upgrade to Windows Server 2025.
Ask your IT team or provider: Which of our systems can be reached from the internet, and does each one need to be? Is multifactor sign-in turned on for every account, especially administrator and remote access accounts? What are we running that no longer gets security fixes?
A good answer sounds like: "We have a list of every system that can be reached from the internet, and a reason each one needs to be. We reviewed it this quarter and switched off what we didn't need. Every account uses multifactor sign-in, including administrator and remote access accounts. Everything out of support has a replacement date, and until then it's kept off the internet."
3. Prevent: would you know if someone got in?
The ACSC asks organisations to monitor systems and applications for suspicious activity, and to find and fix known weaknesses before they can be exploited.[1]
Patching fixes weaknesses once they're known. It doesn't tell you whether an attacker got in before the fix was applied. Monitoring does: it watches your systems for suspicious activity. Regular vulnerability scanning shows which fixes are missing, so nothing slips through.
An attack or suspicious sign-in won't necessarily happen during business hours. Your IT team or provider should be able to detect and respond to suspicious activity at any time, including by locking a compromised account or isolating an infected computer. If that's hard to cover in-house, we can help. efex's 24x7 security operations centre monitors, investigates and contains threats at any hour, stopping an attack on a laptop or server before it spreads.
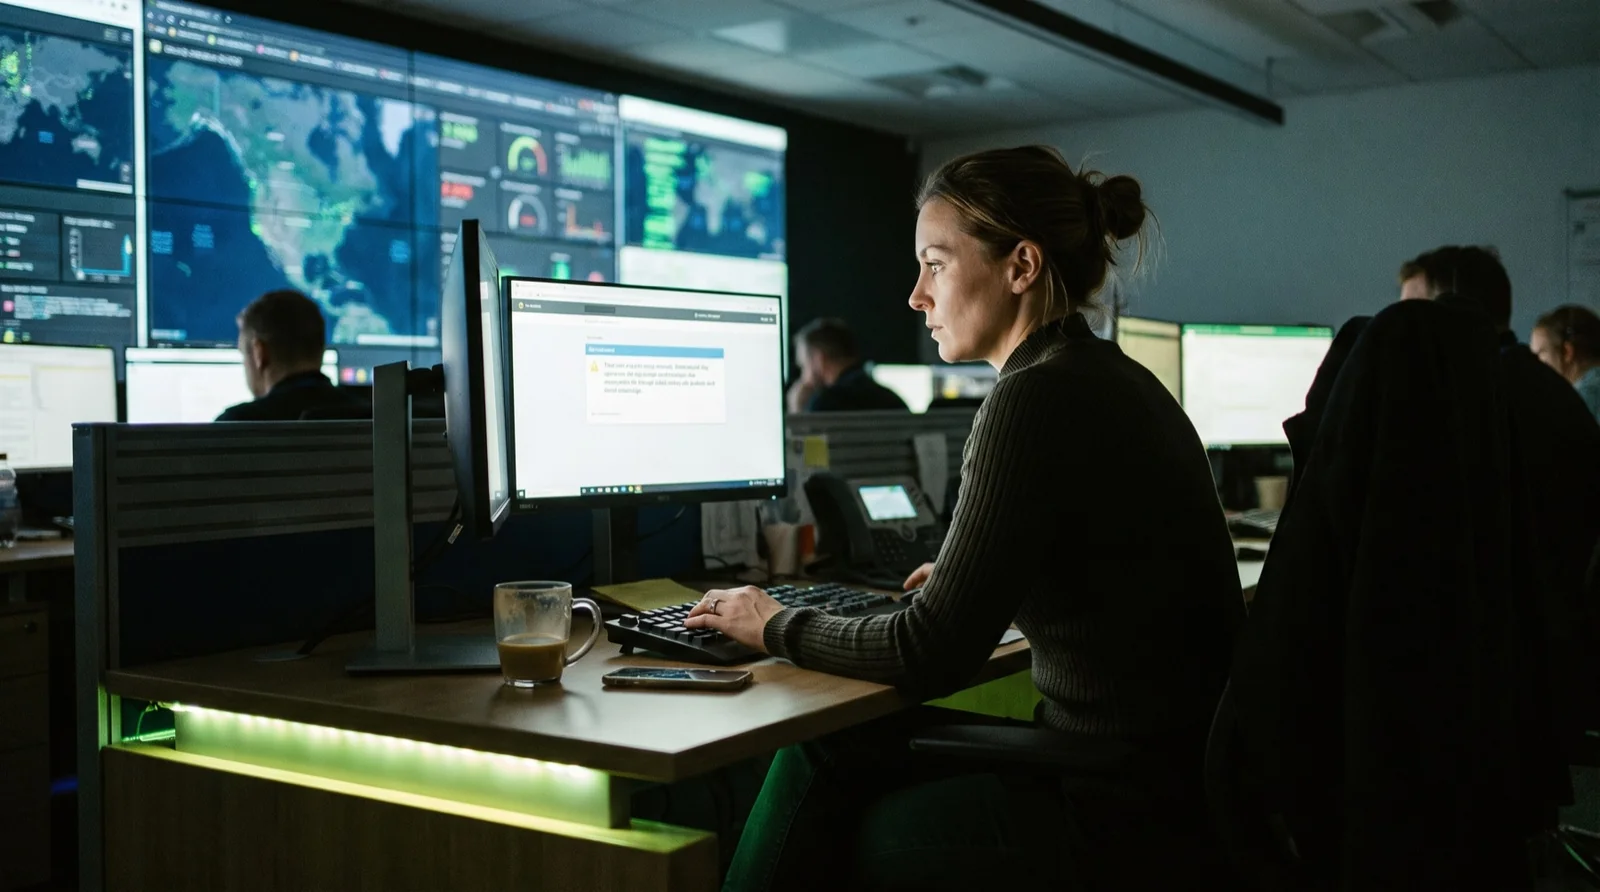
Ask your IT team or provider: Who monitors our systems outside business hours, and can they act immediately without waiting for approval? When did we last scan our systems for known weaknesses, and what did we fix as a result?
A good answer sounds like: "Our systems are monitored around the clock. Whoever is on call can lock an account or take a computer off the network straight away, then call the contact on our list. We scan every month, and the last scan's findings are fixed or have a date."
Act now: five things to do this week
- Today: send the questions above to your IT team or provider and ask for answers by the end of the week. If you're not getting clear answers, speak to one of our experts who are on hand to help.
- Internet-facing systems: check that everything that can be reached from the internet has this month's urgent fixes. If something doesn't, fix it now or restrict access to it until you can.
- Suppliers: ask each supplier that manages your systems, in writing, how quickly they apply urgent fixes, including to the tools they use to manage yours.
- Sign-in: confirm multifactor sign-in is on for every single account, starting with administrator and remote access accounts.
- Approvals and after hours: decide now who can approve an urgent fix that needs a restart during business hours, and who acts on an alert at night or over a weekend.
If you think your organisation has been affected, or you need help, contact the ACSC on 1300 CYBER1 (1300 292 371).[1]
"When the ACSC issues a critical alert, it is asking organisations to act. Check this week how quickly urgent fixes are applied to your internet-facing systems."
Next steps
If you don't have clear answers to the questions above, we're here to help. Book a free cyber audit to review your patching, internet exposure and monitoring, or get in touch with our team if you'd prefer to talk first.
Frequently asked questions
It is the three-part advice in the critical alert the ACSC published on 17 November 2026. Patch: apply urgent security fixes faster, and confirm suppliers can promptly patch the systems they manage for you. Protect: reduce internet exposure, use multifactor sign-in, and replace technology that no longer gets security fixes or protect it until you can. Prevent: monitor for suspicious activity at any hour, and find and fix known weaknesses before attackers exploit them.
ASD has seen some flaws exploited within 48 hours of a fix being released, so you can't rely on a monthly patching cycle for internet-facing systems any more. We recommend applying urgent fixes to firewalls, VPN, remote access, email and websites within 48 hours.
A fix might need a restart during business hours, need testing first, or not have been released yet. Don't just wait. The ACSC advises assessing the risk, restricting exposure and putting temporary security controls in place until the fix is applied. For example, limit who can reach the affected system.
Replace them, or keep them off the internet and away from other systems until you can. The ACSC warns that unsupported systems are easy targets. Windows Server 2016, for example, gets its last regular security fix on 12 January 2027. If you're still running it, now is the time to upgrade to Windows Server 2025.
Yes. The ACSC asks organisations to confirm suppliers can promptly patch the systems they manage on their behalf. Ask your provider in writing how quickly they apply urgent fixes, including to the tools they use to manage your systems.
Many attacks happen at night or over a weekend. Your IT team or provider should be able to spot one at any hour and act on it straight away, for example by locking a compromised account or taking an infected computer off the network. efex runs a 24x7 security operations centre that watches for suspicious activity at any hour of the day or night.
Sources
- Australian Signals Directorate's Australian Cyber Security Centre, "Vulnerabilities are moving quickly, so patch, protect, prevent", alert, 17 November 2026
- Cyber Daily, David Hollingworth, "Act now! Aussie cyber agency warns of growing pace of vulnerability disclosures", 17 November 2026
- Australian Signals Directorate, Annual Cyber Threat Report 2025-26, pp.4, 19, 44-45